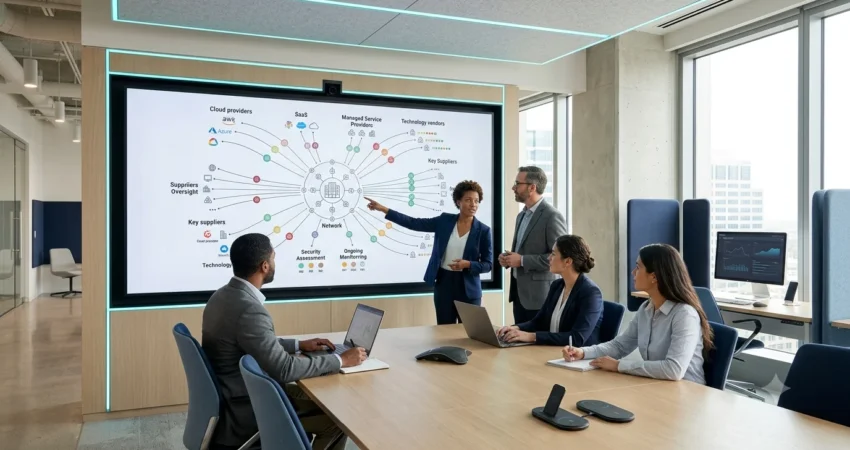
A practical enterprise playbook for classifying suppliers, performing risk-based due diligence, assessing security and compliance, managing findings, strengthening contracts, monitoring third parties, and managing risk throughout the supplier lifecycle.
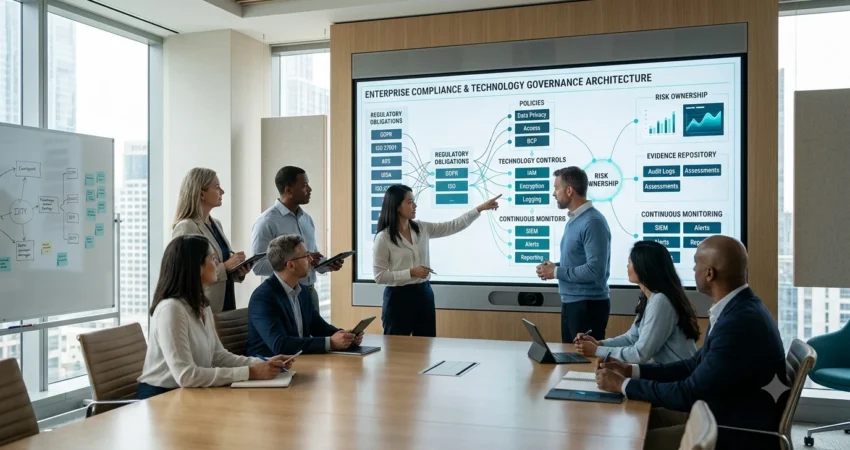
A practical enterprise guide for assessing compliance readiness, translating obligations into controls, establishing evidence, defining ownership, managing gaps, and building sustainable compliance into technology operations.
Learn how KRIs, KPIs, thresholds, and trends can turn technology risk data into executive decision support tied to appetite, control effectiveness, and business impact.
Explore how enterprises can move from periodic compliance exercises toward continuous control visibility, automated evidence, exception management, and stronger operational assurance.
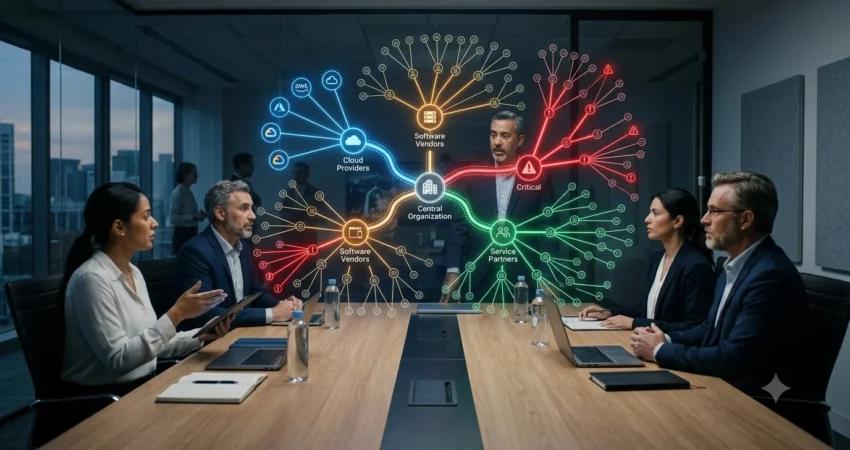
Learn how organizations can evolve third-party technology risk from onboarding questionnaires toward continuous oversight, service dependency analysis, resilience, and decision-ready assurance.
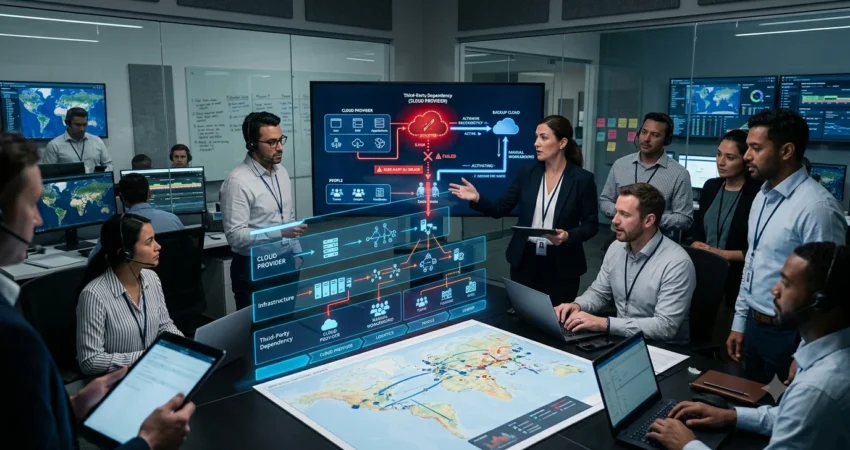
See how operational resilience connects technology risk, third parties, cyber incidents, and continuity testing to the business services customers and regulators actually depend on.
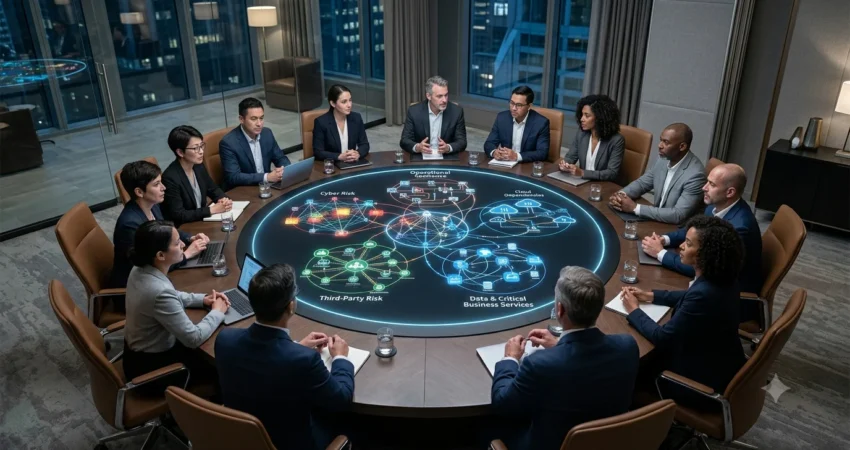
Learn how to integrate technology risk into enterprise governance through a shared taxonomy, controls, ownership, assessment, monitoring, reporting, and exception management.