
Security teams are moving beyond treating every vulnerability as equal toward understanding exploitable attack paths and business-relevant exposure. Leaders should ask which weaknesses can actually reach critical assets.
All Articles

Enterprise cyber defense is increasingly organized around identity rather than network location. Leaders should examine workforce, privileged, machine, and emerging AI-agent identities as one risk surface.

Enterprises are moving AI from conversational assistance toward agents that can plan, use tools, and act in workflows. Leaders should decide how much operational autonomy is acceptable before that shift accelerates.

A practical enterprise guide for planning cloud adoption across strategy, architecture, security, governance, migration, operations, cost management, and continuous optimization.

Learn how enterprises can govern API discovery, authentication, authorization, data exposure, gateway controls, monitoring, and third-party integrations across the API lifecycle.

A practical enterprise playbook for assessing cloud security readiness across identity, configuration, network controls, data protection, workload security, monitoring, governance, resilience, and incident response.

Cloud financial accountability is becoming a shared discipline across engineering, finance, and business teams. Leaders should connect spend to services, rightsizing, and architecture choices without weakening resilience.

Explore how infrastructure resilience should follow workload criticality, redundancy, recovery, observability, and tested dependencies rather than a uniform high-availability label.

Understand how enterprises can move from scanner-driven vulnerability queues to exposure management that uses asset context, attack surface, identity, and threat intelligence to prioritize real risk.

Learn how organizations can evolve security operations from high alert volumes toward stronger telemetry, detection engineering, threat hunting, investigation, and response readiness.
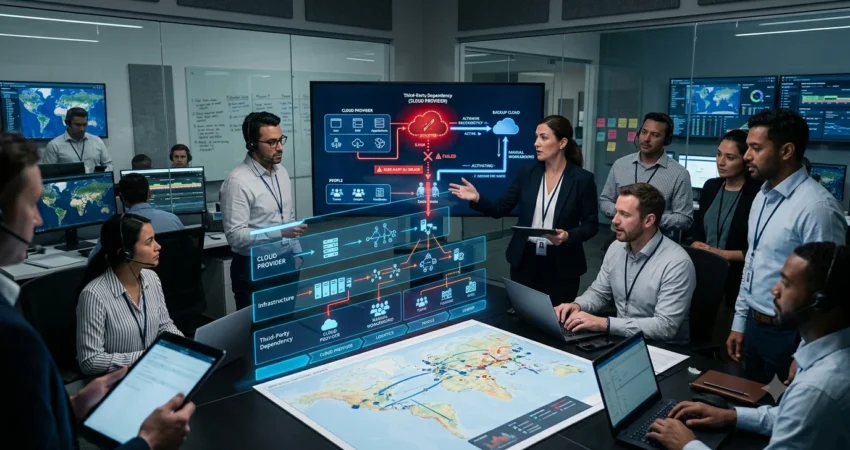

See how operational resilience connects technology risk, third parties, cyber incidents, and continuity testing to the business services customers and regulators actually depend on.

Learn how organizations strengthen cyber resilience through proactive security strategies, governance, Zero Trust principles, and operational readiness to defend against today's evolving cyber threats.